Why Prompt-Only Systems Fall Short
Large language models are often introduced through a chat interface, but industrial systems cannot be governed by conversation alone. A plant, grid, warehouse, or transportation network changes continuously, and every decision depends on current measurements, operating limits, maintenance status, and control authority. The engineering problem is therefore not simply how to write a better prompt; it is how to assemble, validate, and preserve the state that a model is allowed to use.
This shift does not make language models deterministic. Instead, it places a probabilistic component inside a deterministic control envelope. The model may summarize conditions, propose a diagnosis, or rank response options, while software outside the model enforces schemas, physical bounds, permissions, and stop conditions. That division of responsibility is the foundation of state-aware orchestration.
RAG Is Useful, but It Is Not a Control Architecture
Retrieval-augmented generation, introduced in the original RAG research, combines a language model with retrieved external knowledge. It is valuable when a system must locate manuals, procedures, incident histories, or engineering notes. However, a retrieved document does not establish the current state of a physical asset, and similarity ranking does not prove that a source is timely, complete, or applicable to the operating mode at hand.
A production context pipeline should distinguish at least three classes of information: relatively stable knowledge, time-sensitive operational state, and non-negotiable constraints. Stable knowledge can come from controlled document retrieval. Operational state should come from authenticated telemetry and event streams with timestamps, units, quality indicators, and provenance. Constraints should be encoded in software or policy layers that do not depend on the model remembering them.
Treat the Digital Twin as a Governed State Model
NIST describes manufacturing digital twins as synchronized virtual models used to represent, diagnose, predict, and optimize operations, while emphasizing standards, interoperability, verification, validation, and uncertainty quantification. Those requirements matter because a digital twin is not just a live dashboard. It is a governed model of what the system believes about a physical asset, how that belief was formed, and how confident the system should be.
For an AI component, the twin should expose a compact, versioned state snapshot rather than an uncontrolled stream of raw signals. The snapshot can include recent observations, derived features, active alarms, operating mode, maintenance history, and uncertainty. Each field should have a schema, unit, timestamp, source identifier, and validity window so stale or incompatible data can be rejected before inference.
State should also be reproducible. If an engineer reviews an automated recommendation after an incident, the system must be able to reconstruct the exact input snapshot, model version, policy version, retrieved evidence, and tool outputs that informed it. Without that record, neither safety review nor meaningful performance analysis is possible.
Build a Deterministic Control Envelope
The control envelope is the set of mechanisms that limits what the model can observe, infer, and initiate. Input validators reject missing units, impossible values, malformed timestamps, and sensor readings outside declared ranges. Policy checks determine whether an action is permitted for the asset, operating mode, user role, and current risk level. Output validators require the model to return a machine-readable proposal rather than an unconstrained instruction.
Safety-relevant calculations should be performed by deterministic tools, not improvised in generated text. A model can select an approved calculator, simulator, or rules engine and explain its result, but the computed value should come from tested software. When the proposed action affects physical equipment, the system should compare it with interlocks, rate limits, and a known-safe fallback before it reaches a controller.
Formal specification can strengthen this boundary for complex workflows. Leslie Lamport’s overview of specifying and verifying systems explains how state-machine specifications can be checked for safety and liveness properties. The practical lesson is broader than any one notation: critical orchestration rules should be explicit enough to test, simulate, and review independently of the model.
Separate Observation, Reasoning, and Action
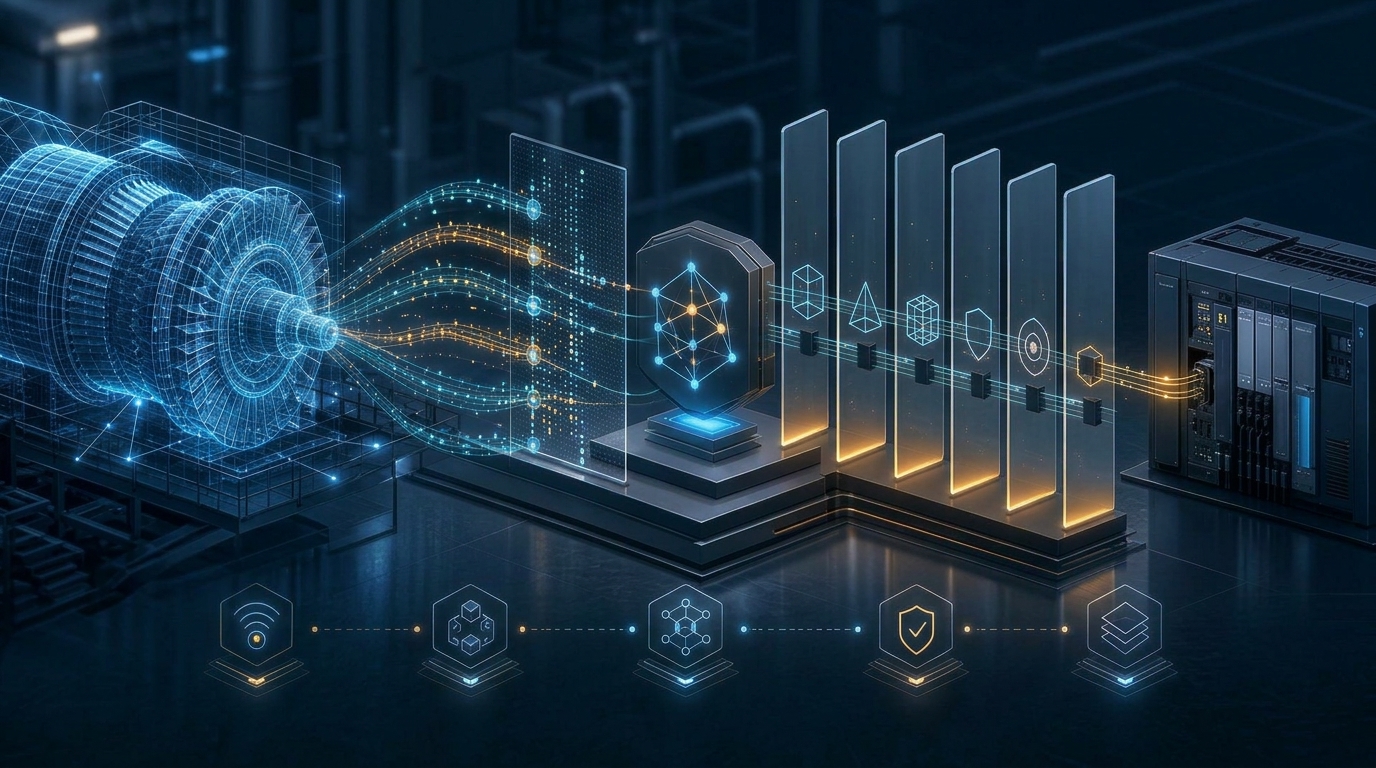
A resilient architecture separates the data plane from the reasoning plane and the action plane. The data plane collects and normalizes telemetry, maintains the current state, and flags uncertainty or loss of signal. The reasoning plane interprets that state, retrieves relevant knowledge, and produces a bounded recommendation. The action plane applies authorization, deterministic checks, and execution controls.
Use Edge and Central Models for Different Jobs
Latency, connectivity, privacy, and compute limits often determine where inference should occur. Small local models or conventional signal-processing algorithms can classify routine conditions close to the equipment, while more capable central models can compare longer histories, coordinate across assets, or assist an engineer with complex diagnosis. The choice should follow measured service-level and safety requirements, not model size alone.
A local fallback should continue to protect the asset when the network or central model is unavailable. That fallback may be a rule set, threshold controller, or previously validated operating mode. Autonomy is credible only when the system degrades safely and makes its degraded state visible to operators.
Measure the System, Not Just the Model
The NIST AI Risk Management Framework organizes risk work around governing, mapping, measuring, and managing AI systems. For industrial orchestration, that means evaluation must extend beyond answer quality. Teams should measure telemetry freshness, schema rejection rates, retrieval relevance, constraint violations, tool errors, human overrides, false alarms, missed anomalies, end-to-end latency, and recovery behavior.
Tests should include normal operation, boundary values, conflicting sensors, stale context, partial outages, adversarial instructions, and simulator disagreement. A recommendation that looks plausible under ideal conditions is not sufficient evidence for deployment. The goal is a documented operating envelope with known limitations and a clear process for responding when those limits are reached.
A Practical Implementation Sequence
Begin with one bounded decision where the current manual process, data sources, and authority boundaries are already understood. Define a canonical state schema and identify which fields are authoritative, derived, uncertain, or optional. Establish a deterministic baseline before adding a language model so the model’s incremental value can be measured.
Next, place the model in advisory mode and log every input, output, tool call, policy decision, and operator response. Use those records to build scenario tests and calibrate thresholds. Only expand autonomy after the system demonstrates stable performance across representative and failure conditions, and retain a human approval step wherever the consequence of error exceeds the organization’s tolerance.
Finally, manage context definitions, policies, prompts, models, and tools as versioned software artifacts. Changes should pass regression tests, security review, and rollback checks before release. State-aware orchestration is an engineering discipline, not a prompt-writing technique, and its maturity is visible in traceability, reproducibility, and controlled failure.
Conclusion: Orchestration Is the Real Interface
The most useful industrial AI systems will not wait for a person to restate the operating environment in a chat window. They will receive a validated representation of current state, consult controlled knowledge, use deterministic tools, and produce bounded proposals that pass independent checks. Their value will come from fitting safely into an engineered workflow, not from sounding confident.
Moving from prompts to state-aware orchestration does not remove uncertainty from language models. It makes that uncertainty visible and manageable by surrounding the model with explicit data contracts, policies, verification, and operational controls. That is the pragmatic path from an impressive demonstration to a dependable production system.