Why identity, consent and eligibility must move at customer speed, even when rewards settle later
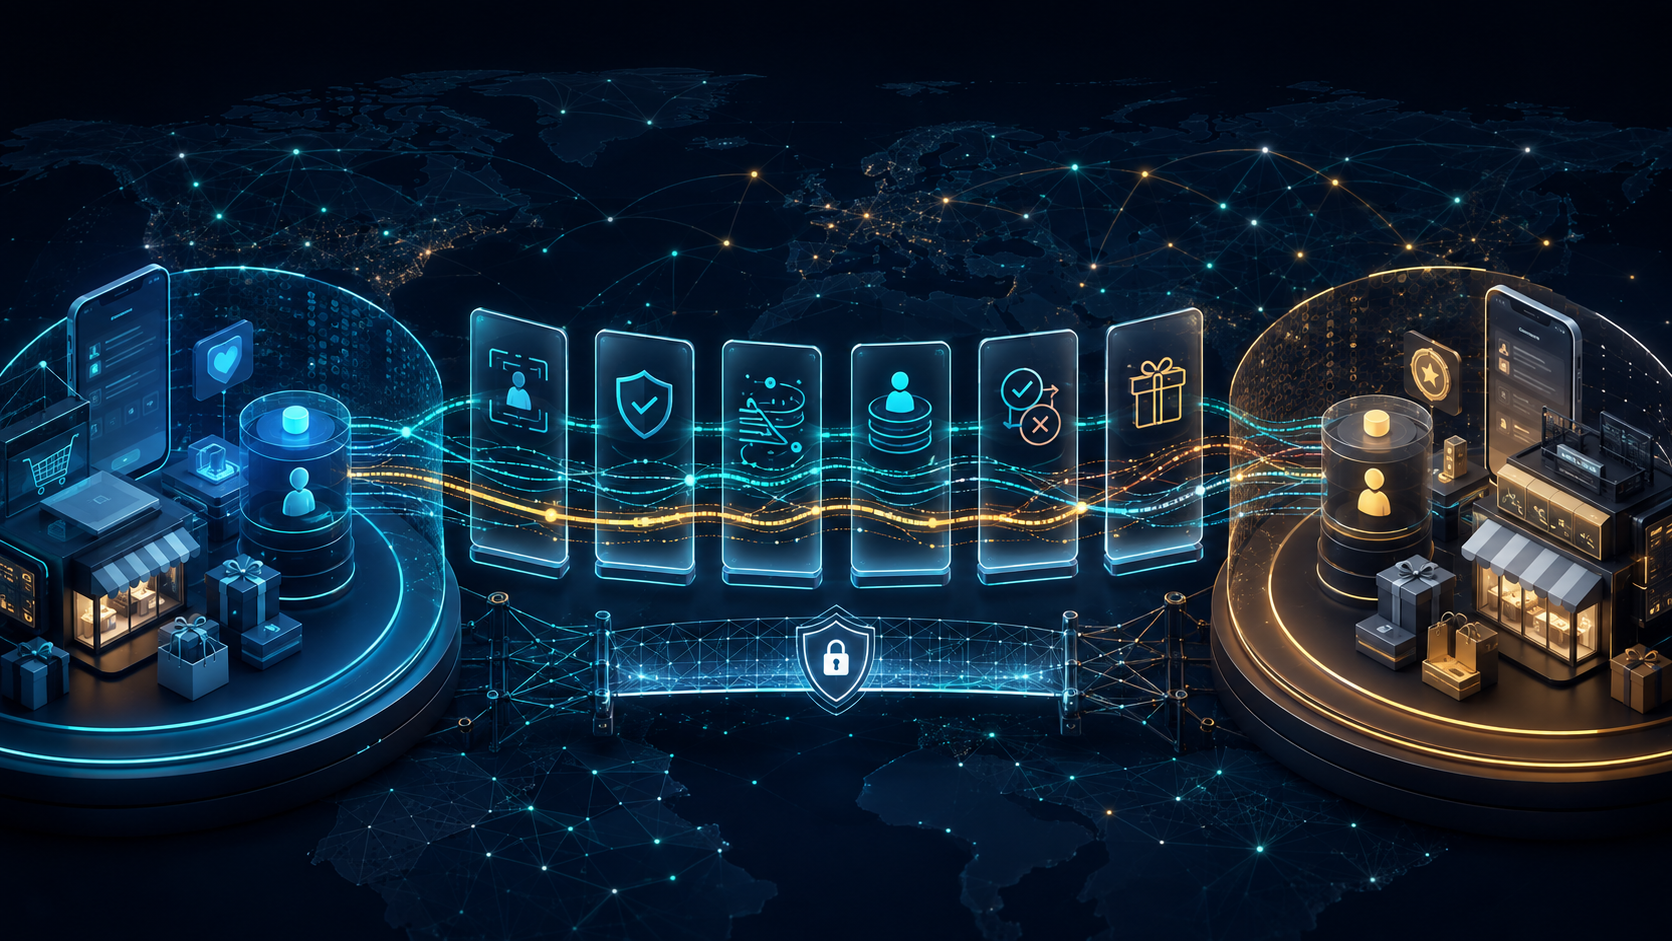
A loyalty partnership looks simple from the customer’s side. Link an account, place an eligible order and earn a reward. The interface may contain only a few taps, but the promise crosses independently operated platforms, identity systems, policy engines and regulatory boundaries.
That promise is also time-sensitive. A points ledger can often settle later. An eligibility decision cannot. If a customer links a loyalty account immediately before placing an order, both platforms must recognise the relationship quickly enough to make the same decision.
In my work on large-scale streaming and batch data platforms, I have found that the hardest integration failures rarely come from moving records from one system to another. They appear when identity, consent, eligibility and partner state move on different clocks.
The core engineering challenge is therefore not points movement. It is establishing trusted customer state across organisational and geographic boundaries at the speed of the customer journey.
The Product Promise Is Synchronous, Even When Settlement Is Not
Traditional loyalty systems were designed around transactions that tolerate delay. Purchases can be collected, reconciled and posted to a ledger in scheduled batches. That model works when the customer only expects a balance to update later.
Account linking changes the contract. Linking becomes part of an interactive product flow, and the new relationship can affect the next decision: whether an offer appears, whether a benefit applies or whether an order qualifies for a reward.
Cross-border programmes add another layer. The same partnership may operate across countries with different consent language, data-sharing restrictions, offer terms and deletion obligations. A globally consistent customer experience must therefore sit on top of regionally controlled policy.
This leads to the first design principle: match data latency to decision latency. Settlement can remain asynchronous, but customer state used for an immediate decision needs its own real-time path.
Separate Decision-Time State From Settlement-Time Ledgers
A practical architecture separates two workloads:
- The decision path answers whether a customer is linked and eligible now.
- The settlement path calculates, reconciles and posts rewards with financial correctness.
The decision path can follow this sequence:
Account-link request -> identity resolution -> consent validation -> canonical event -> stream processor -> customer-state store -> eligibility service -> reward activation
The API receiving the link request should validate the request but avoid becoming the permanent source of truth. It publishes a canonical event, and a stateful stream processor turns that event into a current customer-partner relationship. The eligibility service reads the materialised state rather than rebuilding identity logic on every request.
The same event should also flow to an immutable audit stream. The current-state store answers fast questions. The audit stream explains how the system reached that answer and supports replay, investigation and reconciliation.
A compact event contract might look like this:
{
“event_id”: “01J…”,
“event_type”: “partner_account_linked”,
“customer_id”: “internal-token”,
“partner_account_id”: “partner-token”,
“link_status”: “LINKED”,
“jurisdiction”: “region-code”,
“consent_version”: “2026-08”,
“effective_at”: “2026-08-14T17:42:08Z”,
“source_version”: 17
}
The contract deliberately contains tokens rather than raw account details. It also carries the consent and jurisdiction context used when the relationship was created. event_id supports deduplication, while source_version provides a deterministic ordering rule when delivery order cannot be guaranteed.
An interoperable envelope such as the CloudEvents specification can standardise common event metadata across producers. The business payload and its ownership rules still need a partnership-specific contract.
Treat Account Linking as a Versioned State Machine
A Boolean such as is_linked hides important transitions. A production integration may need to distinguish LINK_PENDING, LINKED, UNLINK_PENDING, UNLINKED and SUSPENDED. These states determine what the customer sees and whether the eligibility service can safely act.
The state transition must be idempotent because partner callbacks, stream retries and replays can deliver the same event more than once. It must also reject stale updates.
function apply(event, current):
if dedupeStore.contains(event.event_id):
return current
if current exists and event.source_version <= current.source_version:
return current
validateTransition(current.link_status, event.link_status)
next = materialise(event)
atomically:
customerState.put(next)
dedupeStore.add(event.event_id)
return next
The atomic boundary matters. If the state update succeeds but the deduplication marker fails, a retry can apply the transition twice. Depending on the storage technology, this can be handled with a transaction, a compare-and-set operation or an idempotent upsert keyed by customer, partner and version.
Unlinking deserves the same care as linking. A late LINKED event must not resurrect a relationship after a newer unlink request. Tombstones or explicit terminal states should be retained long enough to protect the system from delayed delivery and replay.
Build a Latency Budget Around the Customer Decision
“Real time” is not an engineering target. A measurable service-level objective is.
For a journey that must recognise a new link within five seconds at the 95th percentile, an illustrative budget could allocate:
- 500 milliseconds for API and contract validation
- 1 second for event publication and transport
- 2 seconds for processing and state materialisation
- 1 second for eligibility propagation or cache refresh
- 500 milliseconds of safety margin
These are example design targets, not production measurements. The correct budget depends on the customer journey, partner contract and failure policy. The useful exercise is assigning every component a share of the end-to-end objective. Without that allocation, each service can appear healthy while the customer-visible decision still arrives too late.
Eligibility Is a Governed Data Product
Eligibility is rarely a single field. It can depend on whether the accounts are linked, whether the customer is new or returning, subscription state, campaign participation, jurisdiction, partner tier and exclusion rules.
If every application rebuilds those conditions independently, policy drift is inevitable. The mobile experience, checkout service, rewards processor and analytics layer can all reach different answers from the same customer state.
A stronger design publishes eligibility as a governed data product with:
- a named owner
- a documented contract and versioning policy
- defined freshness and availability objectives
- lineage back to identity, consent and programme rules
- a reason code that explains the decision
Reason codes are especially important. INELIGIBLE_REGION, CONSENT_MISSING, PARTNER_ACCOUNT_UNLINKED and RULE_VERSION_UNSUPPORTED are operationally useful in a way that false is not. They improve customer support, monitoring and auditability without exposing sensitive internal details to the customer.
Cross-Border Rules Belong in a Policy Layer
Geography cannot remain a presentation concern. A country code alone is not a policy.
The policy layer should resolve which rule set applies using approved signals such as programme market, account jurisdiction and transaction location. It should return a versioned decision instead of scattering regional conditionals through APIs and user interfaces.
That decision may control:
- whether linking is available in the market
- which consent text and privacy notice apply
- which identifiers can be exchanged or retained
- where customer state may be processed or stored
- which earning and redemption rules apply
- how unlinking, deletion and access requests propagate to the partner
The European Union’s General Data Protection Regulation makes data minimisation a core principle and separately governs transfers of personal data to third countries. Other jurisdictions impose different requirements. The engineering implication is consistent: collect the minimum attributes required for the decision, attach policy context to the state and make deletion a first-class distributed workflow.
Derived attributes also need protection. An eligibility value can reveal that a person belongs to a partner programme even when the underlying identifier is hidden. Access control, retention and observability policies should therefore cover both raw identifiers and derived state.
Design Around Failure States Before the Happy Path
The partnership boundary will fail in ways that an internal service call may not. The partner API can be unavailable, callbacks can be duplicated, events can arrive out of order and one side can accept an unlink while the other remains stale.
A resilient design answers these questions before launch:
- What does the customer see when a link is pending or cannot be confirmed?
- Which system owns the authoritative relationship state?
- Can every operation be retried safely?
- How are poison events isolated without blocking the partition?
- How far back can the stream be replayed?
- How are current-state differences reconciled with the partner?
- What happens when a privacy deletion arrives during an outage?
Dead-letter queues are useful for isolating events that repeatedly fail validation or processing, but they are not a resolution strategy. Every quarantined event needs a reason, an owner, a retry or correction path and an age-based alert. Otherwise the queue becomes a silent second database of unresolved customer state.
A scheduled reconciliation job remains valuable even in a real-time system. Streaming reduces decision latency, while reconciliation detects drift and repairs differences caused by prolonged outages, historical bugs or partner-side corrections.
Observe Business Truth, Not Just Service Health
Infrastructure dashboards can show green while customers receive the wrong answer. Monitoring must therefore validate the business state produced by the pipeline.
Useful service-level indicators include:
- link-to-eligibility freshness at the 50th, 95th and 99th percentiles
- percentage of partner and internal records that agree during reconciliation
- duplicate events suppressed without changing state
- stale events rejected by version checks
- decisions returning an unknown or fallback result
- dead-letter queue volume and age by reason code
- link and unlink completion rates by jurisdiction and rule version
Distribution monitoring can expose failures that latency charts miss. A sudden fall in eligible customers in one region may indicate a policy deployment error, an upstream schema change or a consent-version mismatch. Alerts should point to the affected business dimension as well as the service that emitted the metric.
The Operating Model Is Part of the Architecture
Cross-border partnerships span data engineering, backend services, loyalty operations, product, privacy, security and an external organisation. Technical interfaces alone do not define how those teams respond when the shared state becomes inconsistent.
Each contract needs an owner. Each service-level objective needs an escalation route. Each regional exception needs an approval and expiry process. Incident runbooks should identify who can pause new links, disable a rule version, replay events or initiate partner reconciliation.
This is particularly important during launches. A rollout should start with a small market or customer cohort, compare decisions on both sides and expand only after the state agreement and latency objectives hold. Feature flags control exposure, but the decision logs and reconciliation reports determine whether expansion is safe.
A Practical Blueprint for the Next Partnership
Teams planning a cross-border loyalty integration can start with five steps:
- Map the customer decisions and give each one an explicit latency requirement.
- Separate immediate identity and eligibility state from delayed reward settlement.
- Define a versioned event contract and account-link state machine before choosing infrastructure.
- Design consent, jurisdiction, deletion and reconciliation into the data model before launch.
- Measure end-to-end business correctness and assign operational ownership across both organisations.
The best loyalty integrations do more than move data quickly. They allow two organisations to agree on customer state quickly, safely and explainably enough that the boundary between them disappears from the customer experience.
The partnership remains visible. The plumbing does not.